Disable NGINX HTTP/3 for CVE-2026-95101 and verify the change
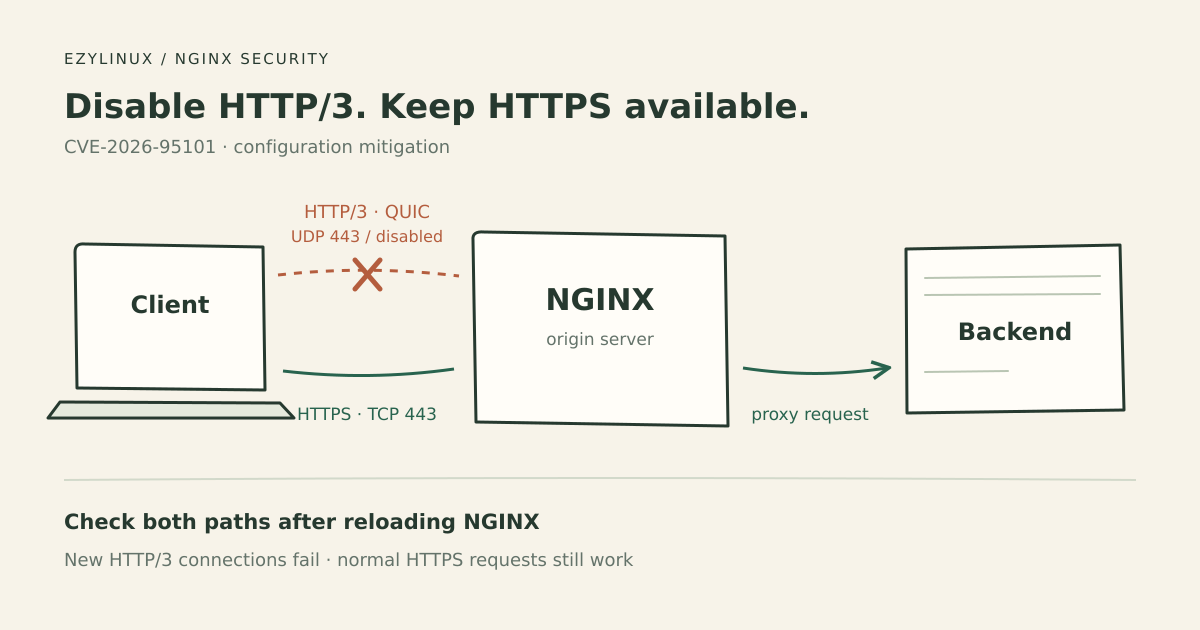
Disable NGINX QUIC listeners to mitigate CVE-2026-95101, compare HTTP/3 and HTTPS before and after, and understand the request-buffering alternative.
3 articles on this topic
Disable NGINX QUIC listeners to mitigate CVE-2026-95101, compare HTTP/3 and HTTPS before and after, and understand the request-buffering alternative.
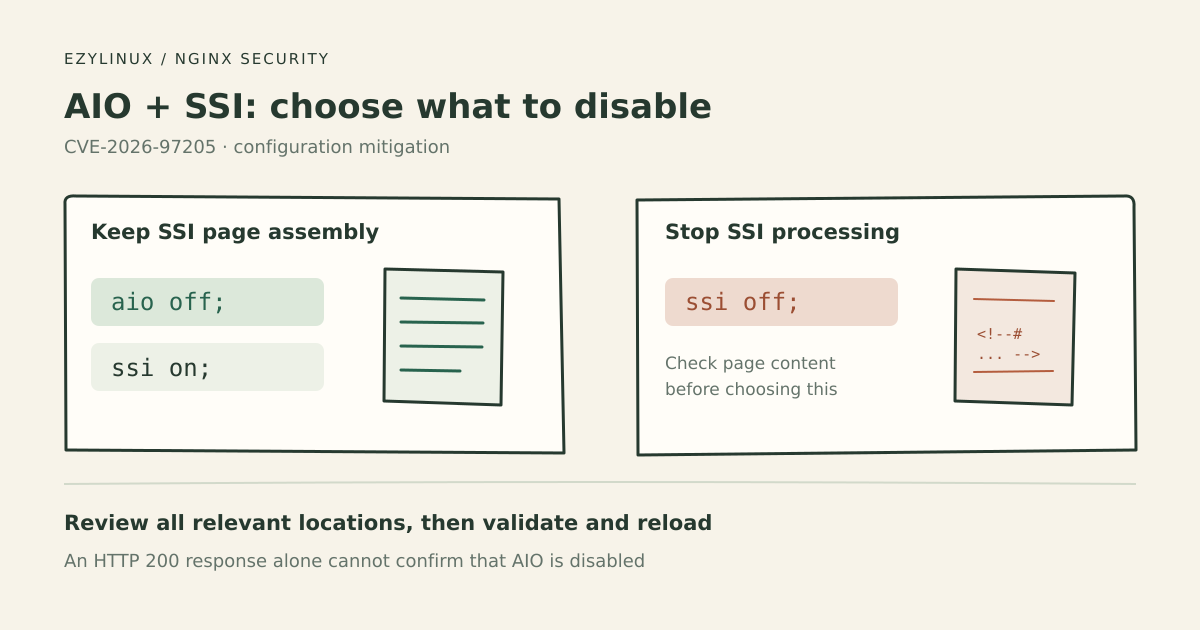
Check NGINX AIO and SSI settings, choose a suitable configuration mitigation for CVE-2026-97205, and verify SSI behavior and AIO configuration coverage.
If curl reports "SSL_ERROR_RX_RECORD_TOO_LONG" after configuring nginx, the server is returning the wrong HTTP protocol: plaintext HTTP instead of encrypted HTTPS.